Hemanth Vishnu Advisory

Prepare for SMB1001 certification

Bring your selected level, practical controls and evidence into one preparation plan for CyberCert’s certification process.

Build on the controls your business operates

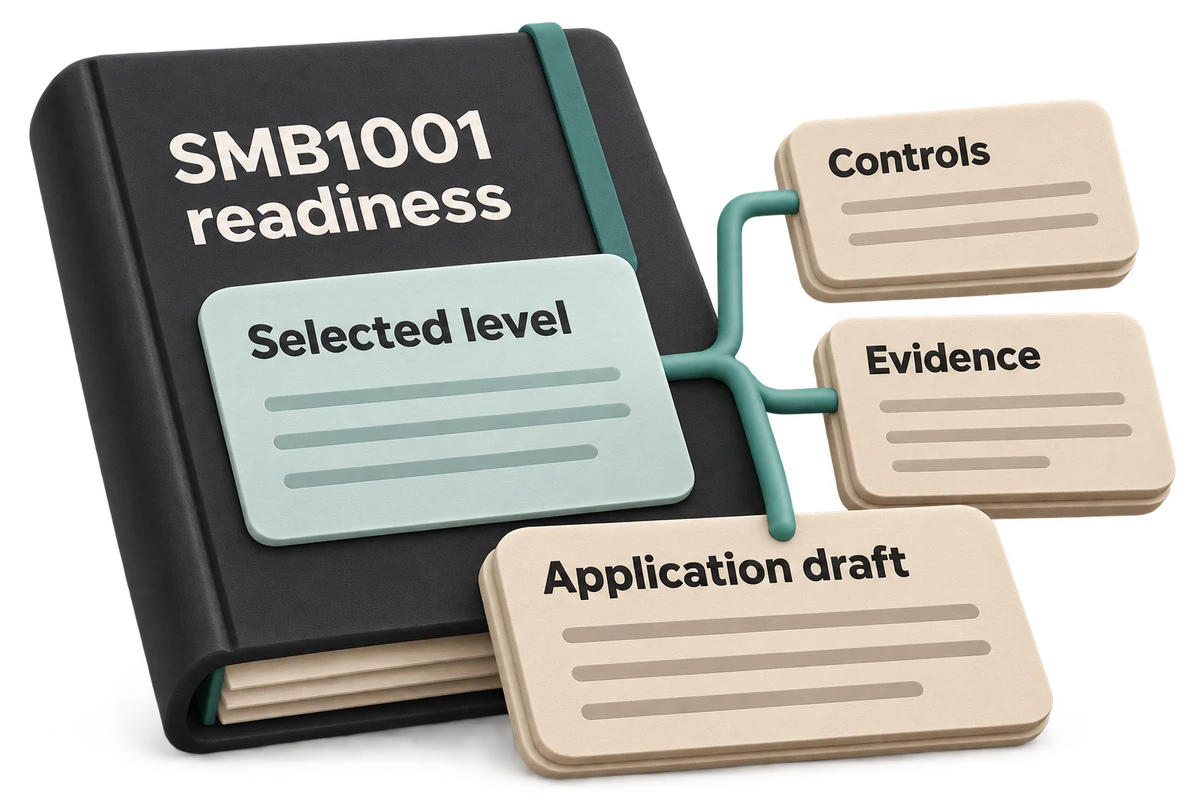
SMB1001 preparation connects a defined certification level with everyday security practices. It gives your business a clearer view of what is in place, what needs improving and which records support the application.

The work brings technical controls, business responsibilities and evidence together. Your organisation can then review its readiness and the remaining actions before progressing through CyberCert’s certification process.

This service can help when:

  • A customer or business objective calls for SMB1001 certification
  • You need to clarify the level and requirements to prepare against
  • Security practices exist, but their coverage or records need attention
  • Your IT provider and business owners need one coordinated action plan

Practical work behind your selected level

Set the right preparation basis

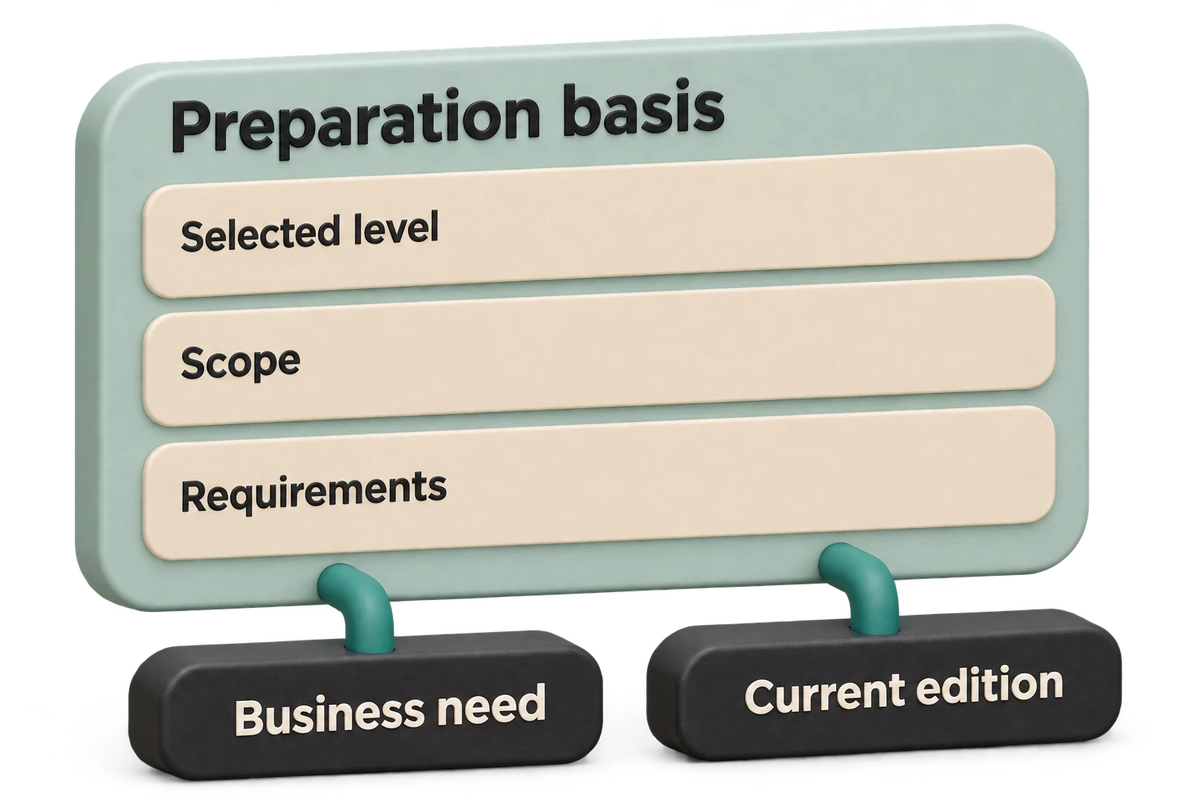
Clarify why your business wants certification and which SMB1001 level it needs. Confirm the current edition, requirements and certification route with CyberCert, then agree the organisation, systems, services and owners included in the preparation.

Use the requirements for that level to organise the review. Identify the relevant technical provider, business decision-makers and records, including any questions that need clarification before the work can be scoped.
Connect requirements with daily practice

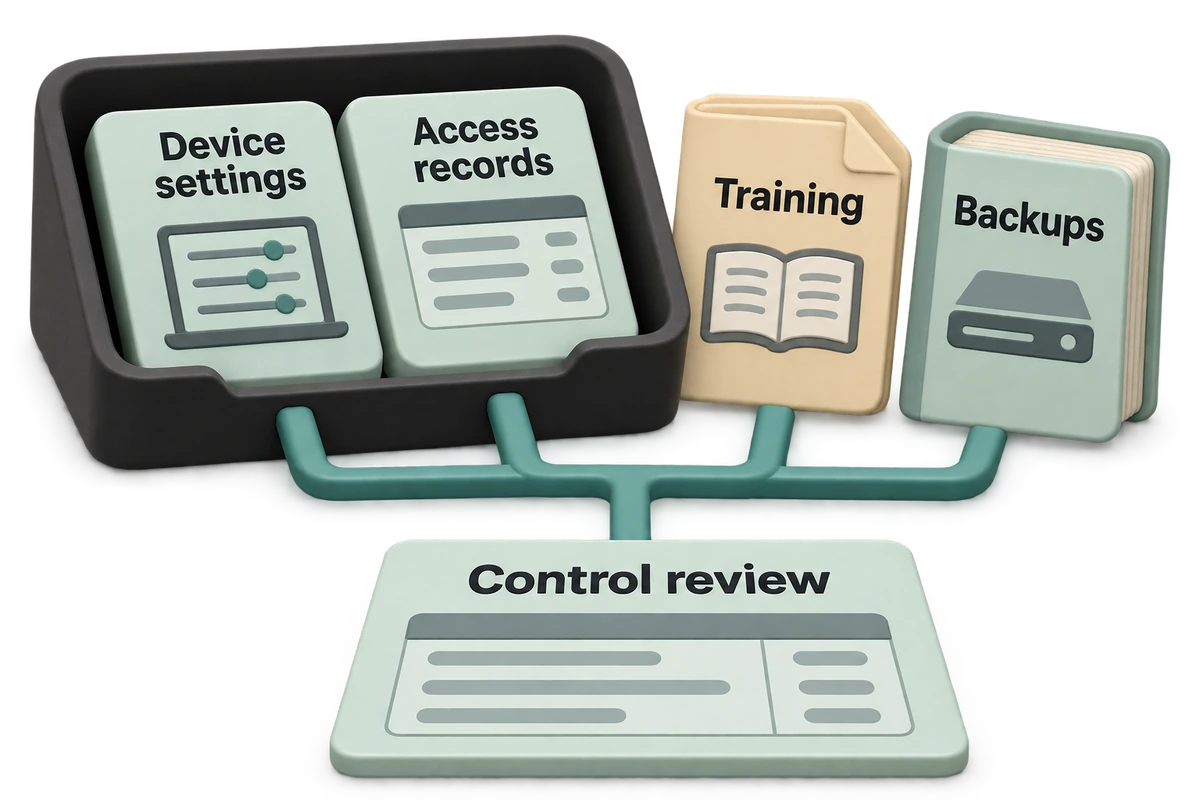
Review the applicable controls alongside the systems, working practices and records that support them. Depending on the selected level, this can include device protection, updates, account access, backups, staff training and the relevant security policies.

Work with the responsible owners to establish what is operating, where it applies and what evidence is available. Connect each finding to its requirement and source record, keeping missing information separate from a confirmed control gap.

Make the remaining work manageable

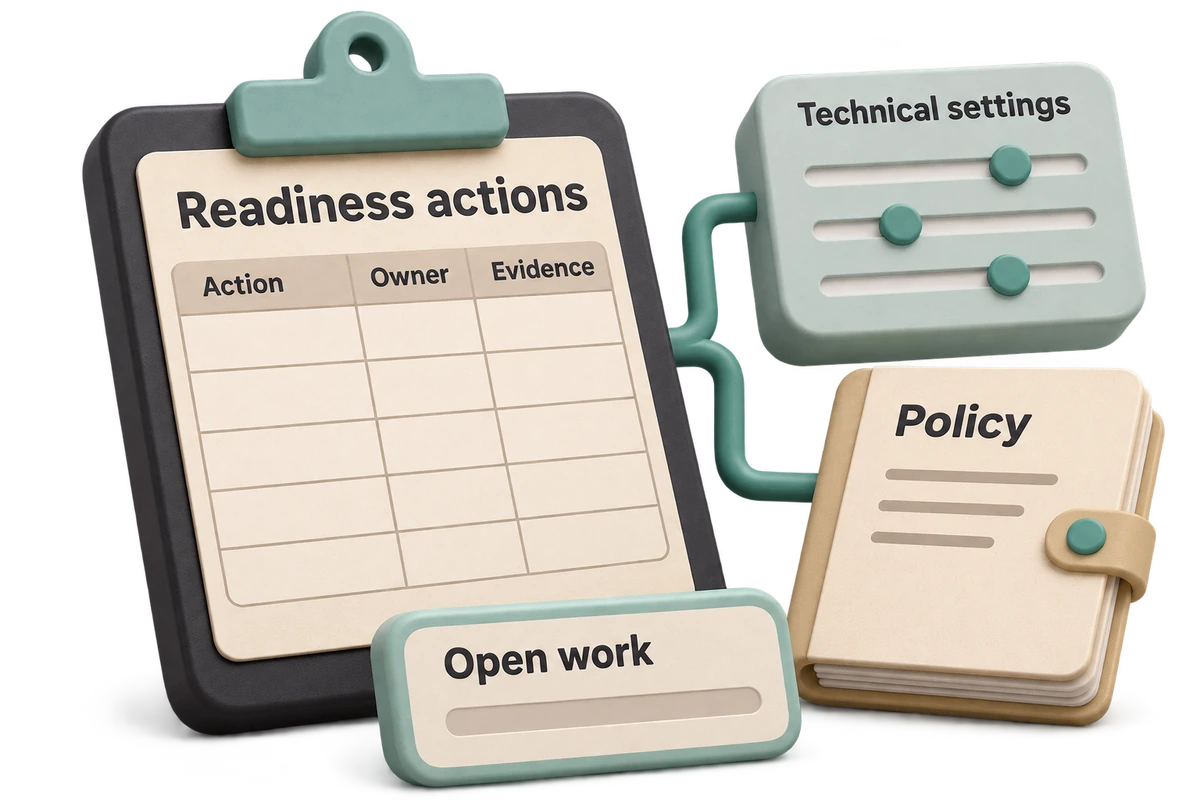
Build a practical action register around the controls and documentation that need attention. Give each agreed action an owner, a priority and the dependencies needed to move it forward, whether it sits with the business, IT provider or another specialist.

Coordinate the agreed technical and process improvements around the access, approvals and change arrangements your environment needs. Keep the record current as work progresses, distinguishing a planned change from an implemented control supported by evidence.

Prepare a submission you can stand behind

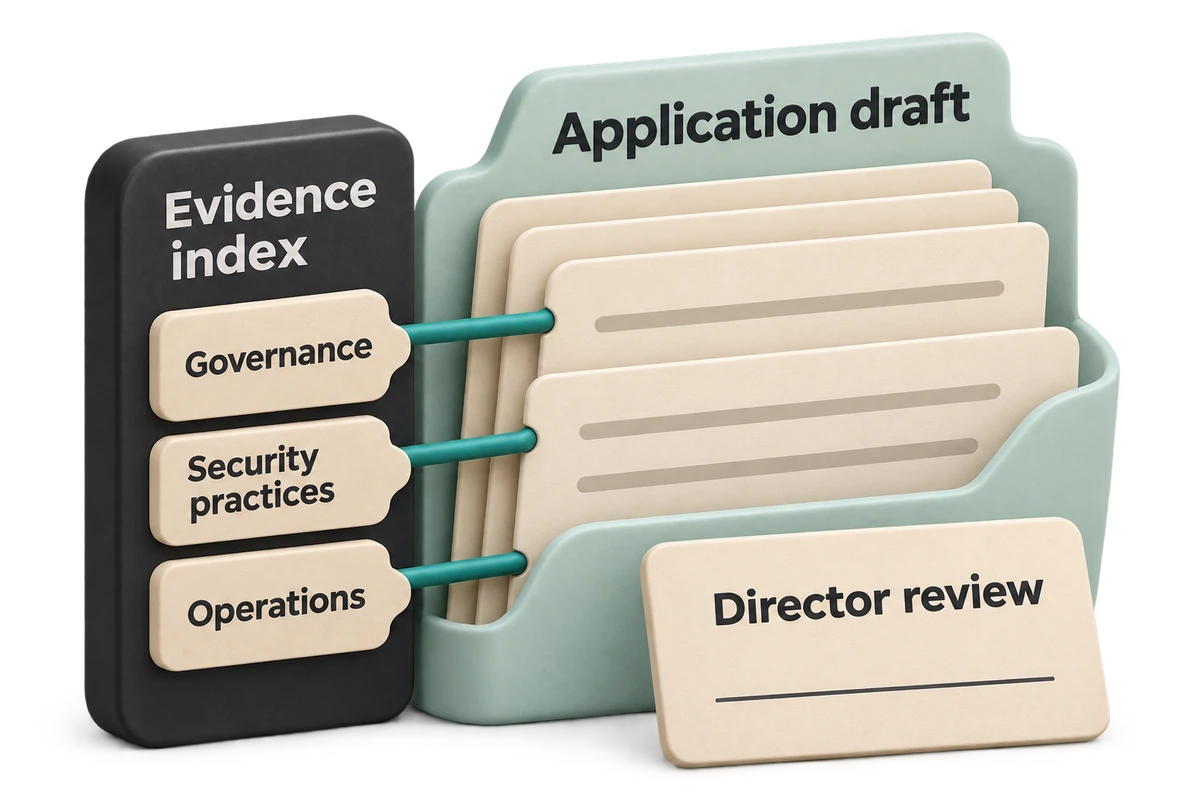
Organise the supporting evidence and application materials around the selected requirements. Check that the responses are consistent with the agreed scope and actual operating practices, with unresolved questions and outstanding work made visible.

Prepare the materials for your organisation’s review before they are submitted through CyberCert’s process. Directors or owners retain responsibility for their attestation and approval of the statements made; preparation helps them see what supports those statements.

A clear record of your preparation

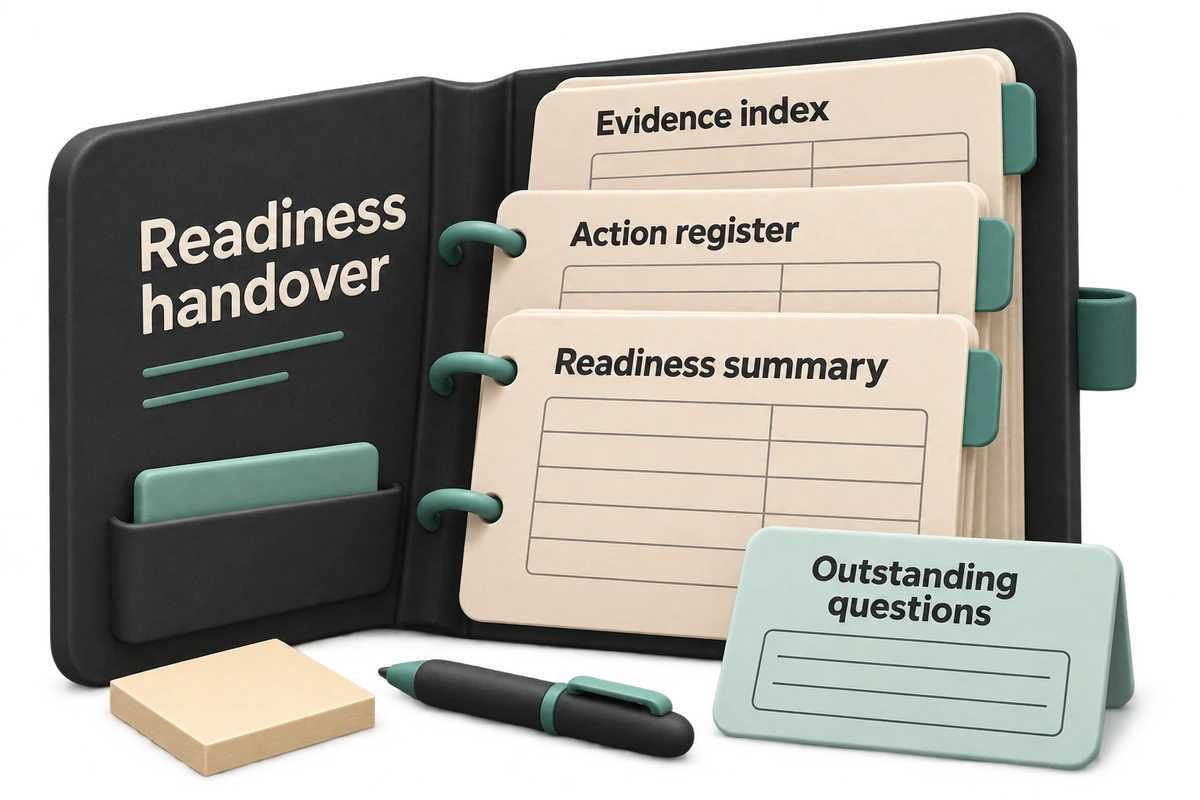
Receive the readiness summary, action register and evidence index, with the agreed application materials prepared for review.

A readiness summary
The selected level, scope and preparation basis, with reviewed controls, findings and outstanding questions clearly recorded.
An owned action register
Practical technical and process improvements, priorities, dependencies and responsibilities for the work still needed.
An evidence index
Supporting records connected to the requirements they address, with missing evidence and limits identified.
Application materials for review
Organised responses and supporting information for your approval, kept consistent with the controls your business operates.

The handover keeps your submission connected to the controls in place, with remaining gaps and decisions visible to the people responsible.

Clear responsibilities from the start

How do SMB1001 and CyberCert fit together?

SMB1001 is a private industry standard developed by Dynamic Standards International. CyberCert provides the certification process and platform used to work towards the selected level.

This service supports the preparation: reviewing controls and records, coordinating agreed improvements and organising evidence and application materials. Certification is issued through CyberCert’s process and remains its decision.

Which level should we prepare for?

CyberCert currently presents five SMB1001 levels: Bronze, Silver, Gold, Platinum and Diamond. The right preparation starts with your business objective, customer requirements and the certification level relevant to your organisation.

Confirm the selected level and current requirements through CyberCert before agreeing the engagement. Work is mapped to that basis, so a review for one level is not presented as readiness for every level.

What will you need from the business and IT provider?

Start with the intended certification level, relevant systems and services, responsible owners and the controls or records already available. The engagement agrees the access and evidence needed for the review.

Technical settings may need input from your IT provider, while training, policies and business procedures need their own accountable owners. Bringing these together helps identify where an apparent documentation gap needs an operational change as well.

Can you help improve the controls?

Yes. The approved service includes an action plan and coordination of agreed improvements. The engagement defines the technical or process work included, who carries it out and the approvals and dependencies involved.

Progress is recorded against the actual changes and supporting evidence reviewed. Work still planned, records not yet available and decisions awaiting an owner remain visible in the readiness summary.

Who approves the application and attestation?

Your organisation approves its application information and the statements made about its controls. CyberCert provides an attestation letter for directors or owners to sign off conformity.

Hemanth helps organise the materials and highlight unsupported or unresolved points. The signatory needs to review the basis for their statements; an evidence index or completed draft does not replace their approval.

Does readiness support include the certification assessment?

Preparation and certification have separate responsibilities. CyberCert’s requirements determine the certification process for the selected level; it currently specifies an external audit for Platinum and Diamond.

Confirm the assessment, audit and provider requirements before starting, including the separate work and fees involved. Hemanth supports preparation and agreed improvements; certification and any required external assessment follow CyberCert’s process.

How will we work together?

You work directly with Hemanth. Remote delivery is the default, with working overlap, meetings, system access and review points agreed around the preparation needed.

Your business and IT owners provide the relevant input and retain approval of changes and disclosures. Further improvement work or continuing support is scoped separately around the work your business needs.

Let’s put your preparation in order

Talk through your selected level and agree a practical next step.