Hemanth Vishnu Advisory

Prepare for CPCSC Level 1

Connect your contract requirement, security controls and evidence in a clear preparation plan for your organisation’s Level 1 self-assessment.

Make your preparation clear and accountable

The Canadian Program for Cyber Security Certification helps protect specified government information handled by suppliers. Where Level 1 applies, preparation connects the contract requirement with the systems, controls and evidence behind the self-assessment.

The work gives your organisation a documented readiness position and a practical improvement plan. Your authorised representative can review what supports the responses and what still needs attention before attesting.

This service can help when:

  • A Canadian procurement or contract identifies a CPCSC Level 1 requirement
  • The information, systems and people in scope need clarifying
  • Your IT owners need a practical plan for controls and missing evidence
  • Your authorised representative needs supported self-assessment responses

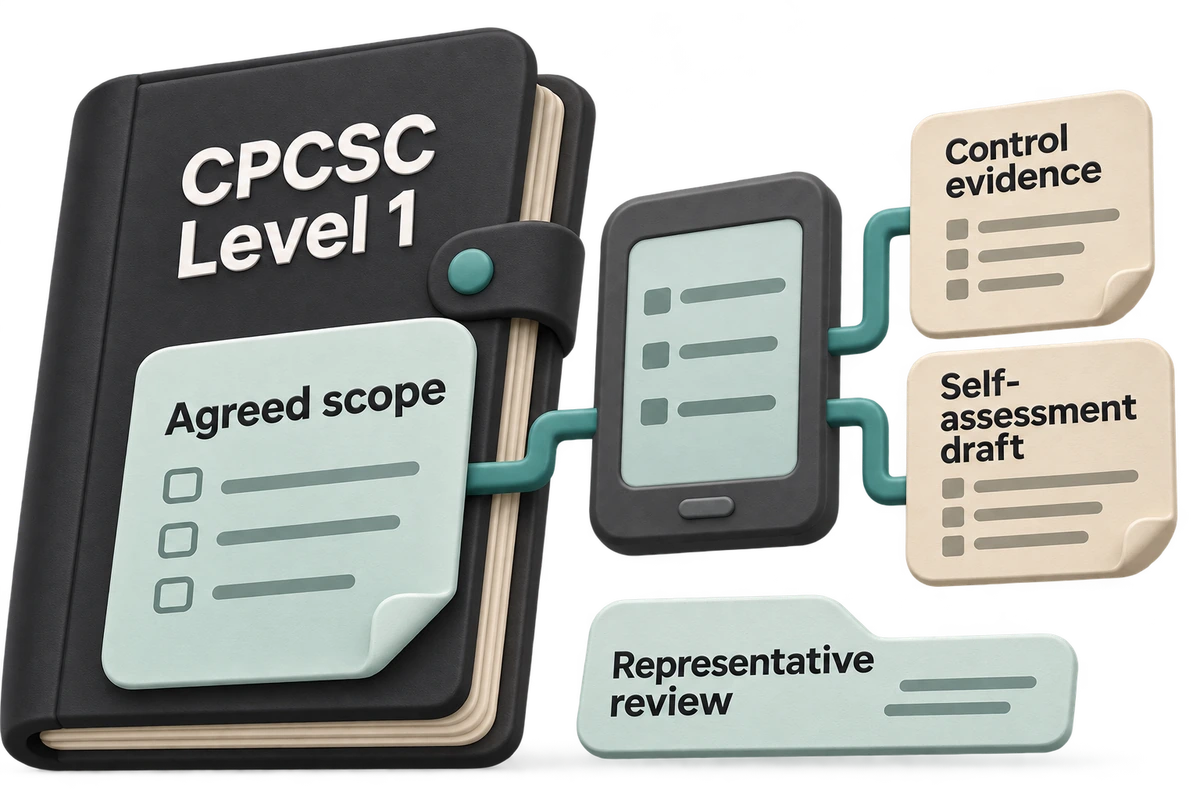
From contract requirement to supported answers

Define what the assessment covers

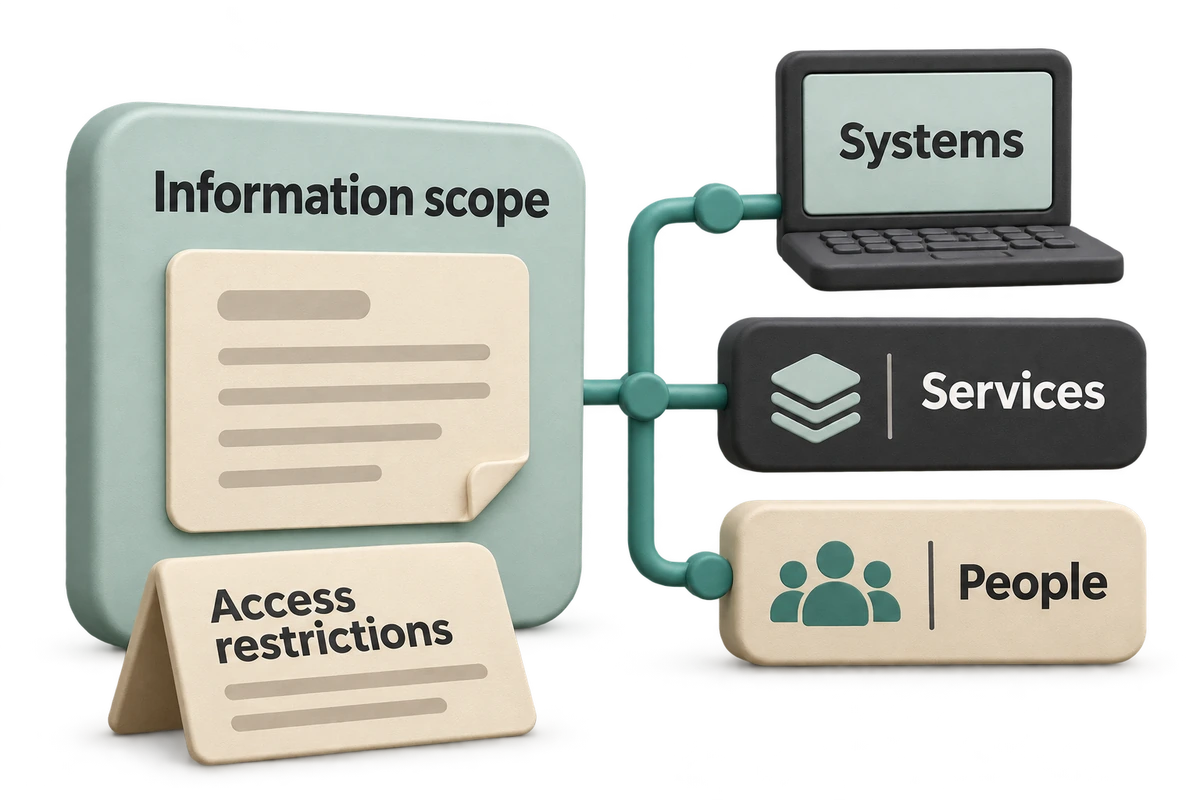
Start with the requirement in your procurement or contract and the information it identifies for protection. Map where that information is handled or stored, the systems and services involved, and the people who can access it.

Agree the proposed boundary and responsible owners before reviewing controls. Check contractual, data-access and residency restrictions before records are shared or system access is arranged, including what can be reviewed remotely and where specialist clarification is needed.
Review the Level 1 controls in practice

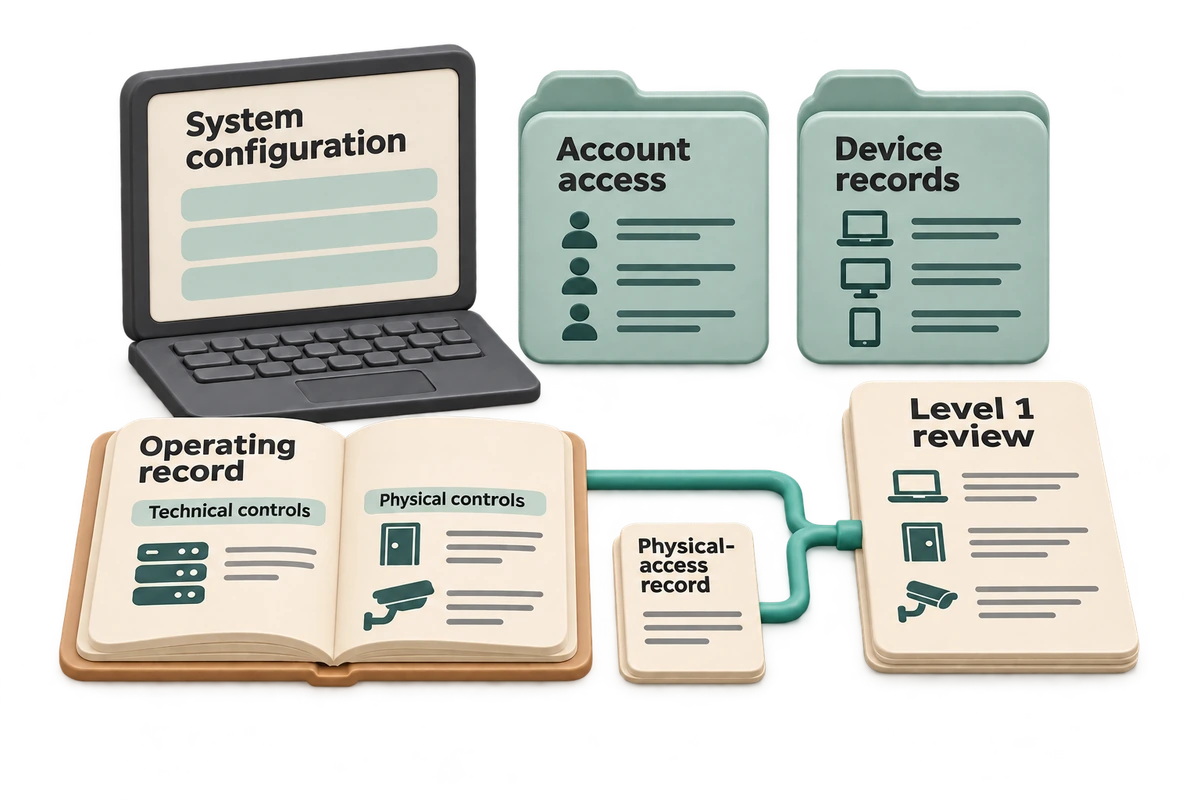
Review the 13 Level 1 requirements across access control, identification and authentication, media protection, physical protection, network protection and system integrity. Use the official criteria to connect each requirement with the people, settings and records in scope.

Examine relevant account and device records, access reviews, operating rules, update records and security configuration. Discuss how the controls work with the responsible owners and agree any necessary checks, recording gaps in implementation separately from information still needed.

Give each gap a practical next step

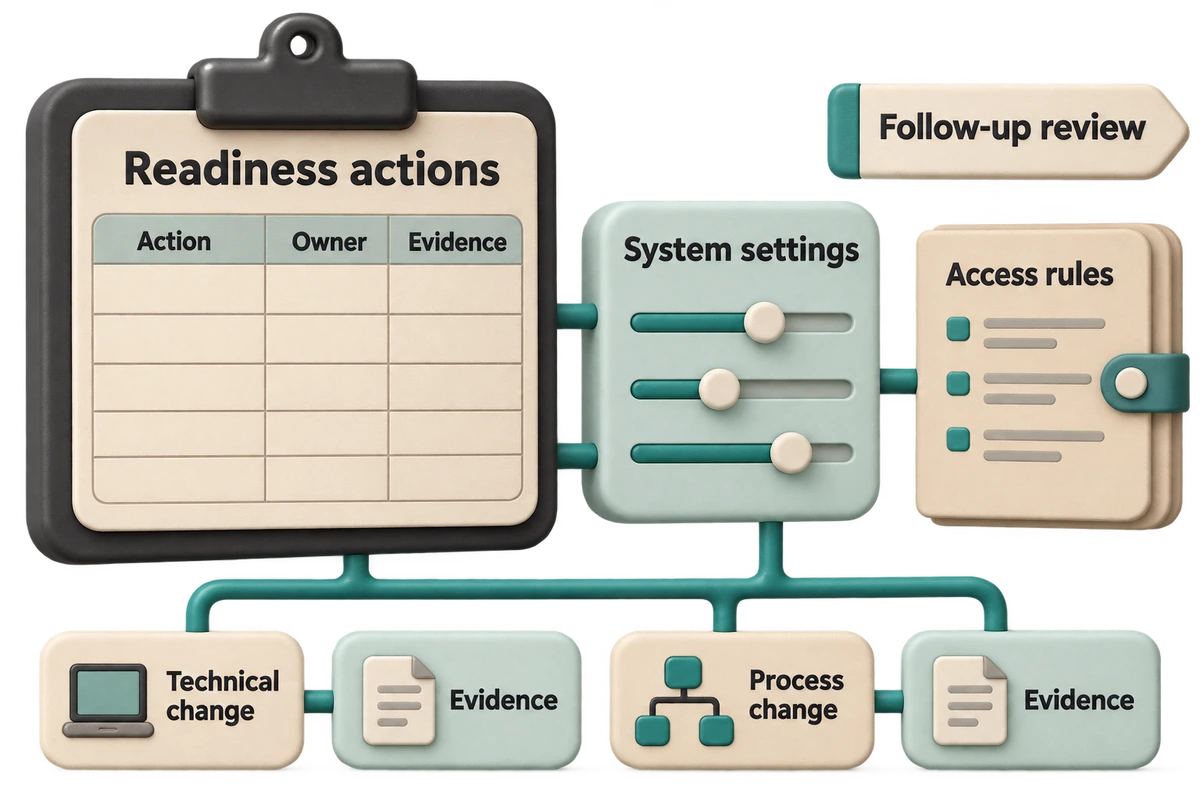
Turn the findings into an action register with priorities, owners and dependencies. Agree which technical changes, working practices or records need attention, and which actions sit with your business, IT provider or another specialist.

Coordinate the improvements included in the engagement around the access and approvals available. Record the changes and follow-up evidence reviewed, keeping outstanding actions visible so the self-assessment reflects the controls actually operating.

Prepare responses your representative can review

Organise the evidence and draft self-assessment responses against the agreed Level 1 scope. Check that the answers are consistent with the records and working practices reviewed, with uncertain points and remaining work clearly identified.

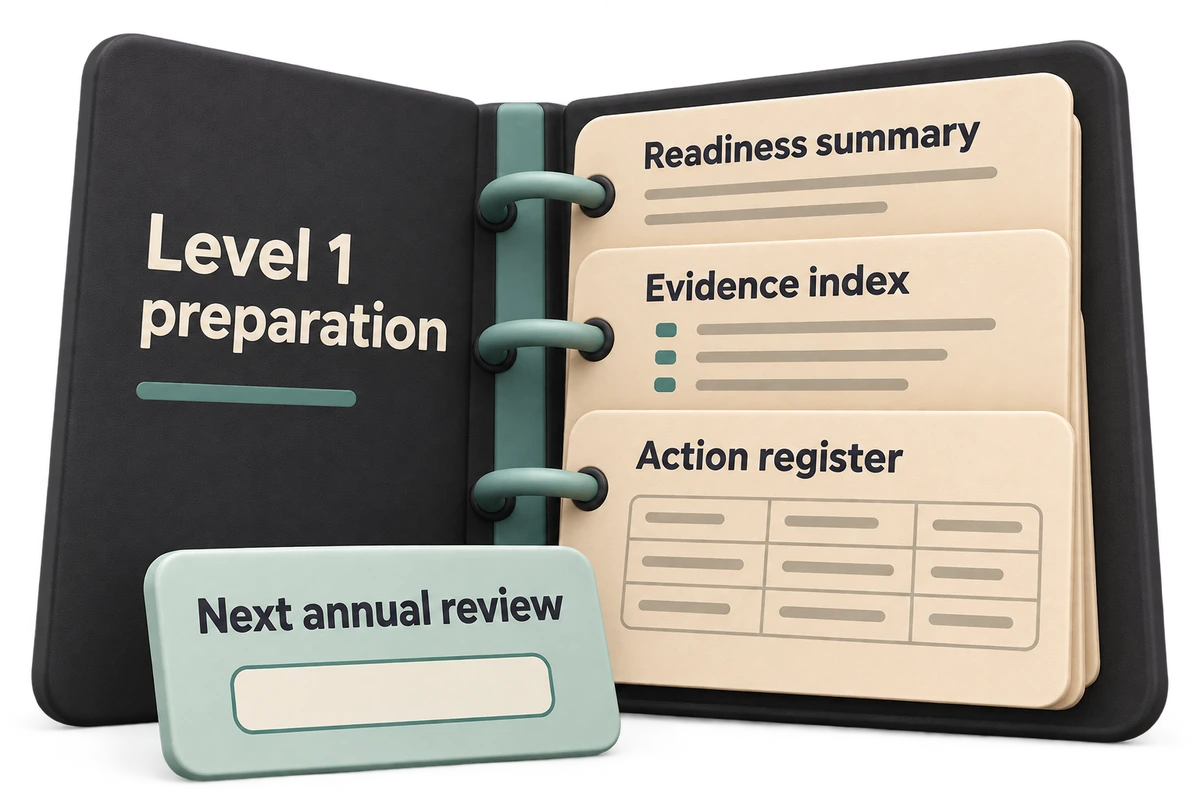
Provide your authorised representative with the readiness summary, evidence index and action register for review. Your organisation owns its attestation and submission, retains its results and expiry information, and keeps the supporting evidence available for the required cycle.

A clear record for review and upkeep

Receive an evidence index, readiness summary and action register, with the agreed self-assessment materials prepared for review.

A scoped readiness summary
The contractual preparation basis, proposed assessment boundary, reviewed controls and remaining gaps or questions.
A mapped evidence index
Records connected to the Level 1 requirements, systems and owners they support, with missing evidence clearly identified.
An owned action register
Prioritised improvements, dependencies and responsibilities, with agreed progress and outstanding work recorded.
Self-assessment materials for review
Draft responses and practical upkeep actions for your authorised representative’s review and the next annual assessment.

The handover connects each reviewed requirement with its evidence and owner, and keeps the work needed after submission visible.

Clear responsibilities from the start

When does CPCSC Level 1 apply?

The requirement comes from the applicable procurement or contract. Canadian guidance identifies Level 1 for selected contracts; it is not automatically required for every defence supplier or every contract.

Confirm the required level, information to protect and procurement instructions with the relevant authority before agreeing preparation. This service supports the Level 1 requirement established for your organisation’s work.

What is included in the Level 1 review?

Level 1 covers 13 requirements drawn from Canada’s ITSP.10.171 standard. The review uses the published Level 1 criteria and the agreed scope, including the relevant technical settings, working practices and physical safeguards.

The engagement identifies what will be examined, discussed with owners or checked, and the access needed. Findings remain limited to that coverage and the evidence available, with unresolved questions visible in the readiness summary.

Who completes and approves the self-assessment?

Your organisation is responsible for its self-assessment and attestation. Hemanth helps prepare the scope, control records and supported responses for your authorised representative’s review.

The organisation retains the results and expiry information and follows the applicable CanadaBuys and procurement instructions. Readiness support does not replace the representative’s approval or the organisation’s responsibility for the statements made.

Can you help implement the improvements?

Yes. The approved service includes identifying gaps and coordinating agreed improvements with your IT owners. The engagement defines the technical or process changes included, the person carrying them out and the access, approvals and dependencies involved.

Progress is recorded from the changes and supporting evidence reviewed. A planned action is kept distinct from a control that has been implemented and can support a self-assessment response.

How are remote access and sensitive records handled?

The engagement checks access, residency and contractual restrictions before any information is shared or system access is granted. The contract and responsible authority determine what can be made available and from where.

Agree the permitted review arrangements with your organisation first. Where access is restricted, identify the input needed from authorised local owners and any specialist dependencies before committing to the review coverage.

What needs maintaining after the self-assessment?

Level 1 uses an annual self-assessment where it applies. Canadian guidance says to keep evidence through the attestation cycle, for at least one year. Keep results, expiry information and the records supporting the responses available.

Assign owners for control upkeep, evidence updates and changes to the systems or information in scope. The handover identifies practical follow-up actions; continuing support can be agreed around the work your organisation needs.

Does this include higher CPCSC levels or CMMC?

This service covers CPCSC Level 1 preparation. Higher-level certification work and a separate US CMMC engagement need their own scope and requirements.

If you already hold CMMC certification, Canadian guidance allows case-by-case recognition after the relevant scope is checked. Confirm acceptance with the responsible Canadian authority; existing evidence can be considered without assuming automatic recognition.

Let’s put your Level 1 preparation in order

Talk through your requirement and agree a practical next step.